Secure AI Agents,
Engineered for Trust.
We design and deploy production-grade AI agents inside your cloud. Numbers come from your data, not the model. Every outbound action waits for a human, and every step is traceable.
Built on production infrastructure
The problem
Most GenAI pilots never reach production.
Usually the model isn't the problem. The system around it wasn't built for an enterprise to trust.
The demo doesn't survive security review
A notebook with an API key isn't something your CISO can approve. Identity, data access and approvals were never designed in.
Nobody can audit the numbers
If a model produced the figure, nobody can reproduce it. Finance, sales and compliance teams stop trusting the output quickly.
Costs and behavior drift after launch
Without tracing, token caps and evals, the system you approved slowly stops being the system that's running.
Agent suites
Proven agent systems, ready to adapt to your business.
We build these for ourselves and for clients. Each one starts a new engagement from working code rather than a blank page.
CMO Agent Suite
A marketing team of agents that finds, scores and engages pipeline, and never publishes without sign-off.
CFO Agent
Finance analysis at agent speed, with every figure traceable to the query that produced it.
Red-Team Agent
Adversarial testing for your LLM apps and agents, before your users (or attackers) do it for you.
Trust & Safety Triage
A detect-and-escalate pipeline that classifies content and routes cases to human reviewers. It never takes enforcement action on its own.
How we build
Trust is an architecture, not a prompt.
Instructions can be ignored or worked around. We put each guarantee where the model can't reach it: in IAM, in SQL, in runtime plugins and in CI.
Numbers never come from a prompt
Scores, forecasts and totals are computed in versioned, parameterized SQL. The model chooses what to ask for; it has no mechanism to produce the figure itself.
External actions wait for a human
Publishing, posting, paying and emailing are halted at runtime by a platform-level gate. Approvals are bound to the exact arguments and expire.
Agents cannot approve themselves
Approval lives outside the agent's toolset and is reachable only by an authenticated person. It's enforced by IAM, not by instructions.
Least privilege, per tool
The runtime identity holds no data permissions. Each tool impersonates its own narrowly scoped service account at call time. No keys on disk.
Spend is bounded twice
An in-process token cap stops a runaway call before tokens are spent, and a budget alert catches drift across runs.
Every step is traceable
Routing, tool calls and gate decisions land on one OpenTelemetry trace, so you can audit why an agent did what it did.
Capabilities
The engineering behind every agent.
We connect the AI demo to production-grade infrastructure.
Autonomous Enterprise Agents
Multi-agent systems that plan and execute real workflows, with humans in control of anything that leaves the building.
Model Context Protocol (MCP) Integration
Connect models to proprietary data and APIs without copying that data somewhere it shouldn't be.
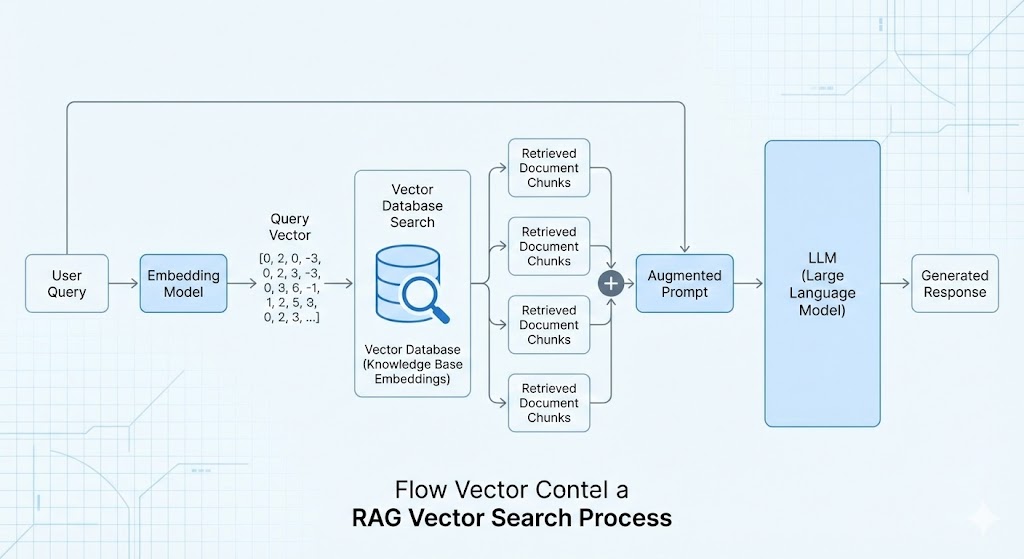
Enterprise RAG Pipelines
Retrieval over your PDFs, spreadsheets and databases, with an evaluation harness to prove it's retrieving the right thing.
GraphRAG & Knowledge Mapping
Multi-hop answers over entities and relationships that flat vector search can't handle.
Deterministic Extraction Engines
LLMs are probabilistic. Your ledger isn't. We keep the arithmetic in the database.
LLMOps & Observability
Day 2 is harder than Day 1. Traces, cost controls and evals from the first deploy.
How we engage
From first workshop to production, in weeks.
Every engagement follows the same five phases, scoped to where you are today.
- 01Discover1–2 weeks
- 02Blueprint1–2 weeks
- 03Build4–8 weeks
- 04Harden1–2 weeks
- 05OperateOngoing
AI Readiness Sprint
2 weeksFor teams deciding where GenAI fits. We assess your data, workflows and risk posture and deliver a prioritized roadmap with an architecture sketch for the top use case.
- —Use-case prioritization
- —Data & security assessment
- —Reference architecture
Agent Pilot
6–10 weeksFor one high-value workflow. We design, build and harden a production-grade agent system in your cloud, starting from one of our suites or from scratch.
- —Production-grade build
- —Evals & red-team report
- —Go-live in your environment
Scale & Operate
OngoingFor organizations running several agents. Shared platform, approval UI, observability, and continuous red-teaming as you add use cases.
- —Agent platform & governance
- —Managed LLMOps
- —Continuous red-teaming
Who we serve
Enterprise rigor, sized for mid-market.
Whether you have a platform team of fifty or a single data engineer, the controls that make agents safe are the same. We scope the work to match.
Financial services
Deterministic numbers, audit trails and approvals for anything that moves money.
Healthcare & life sciences
PHI stays in your environment, with scoped access and redacted logs.
B2B & professional services
Pipeline, content and proposal agents that respect brand and approval workflows.
Public sector & compliance
Detect-and-escalate systems where humans make every consequential decision.
“Most consultancies show you a demo in a notebook. We show you a Docker container running in your VPC.”
Ready to put an agent into production?
Tell us about the workflow. We'll tell you honestly whether an agent is the right answer, and what it would take to make it safe.